Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
HumanSignal label-studio
Affected versions
| Product | Affected | Fixed in |
|---|---|---|
| label-studio PyPI |
|
|
Original description
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
1. Create a project. 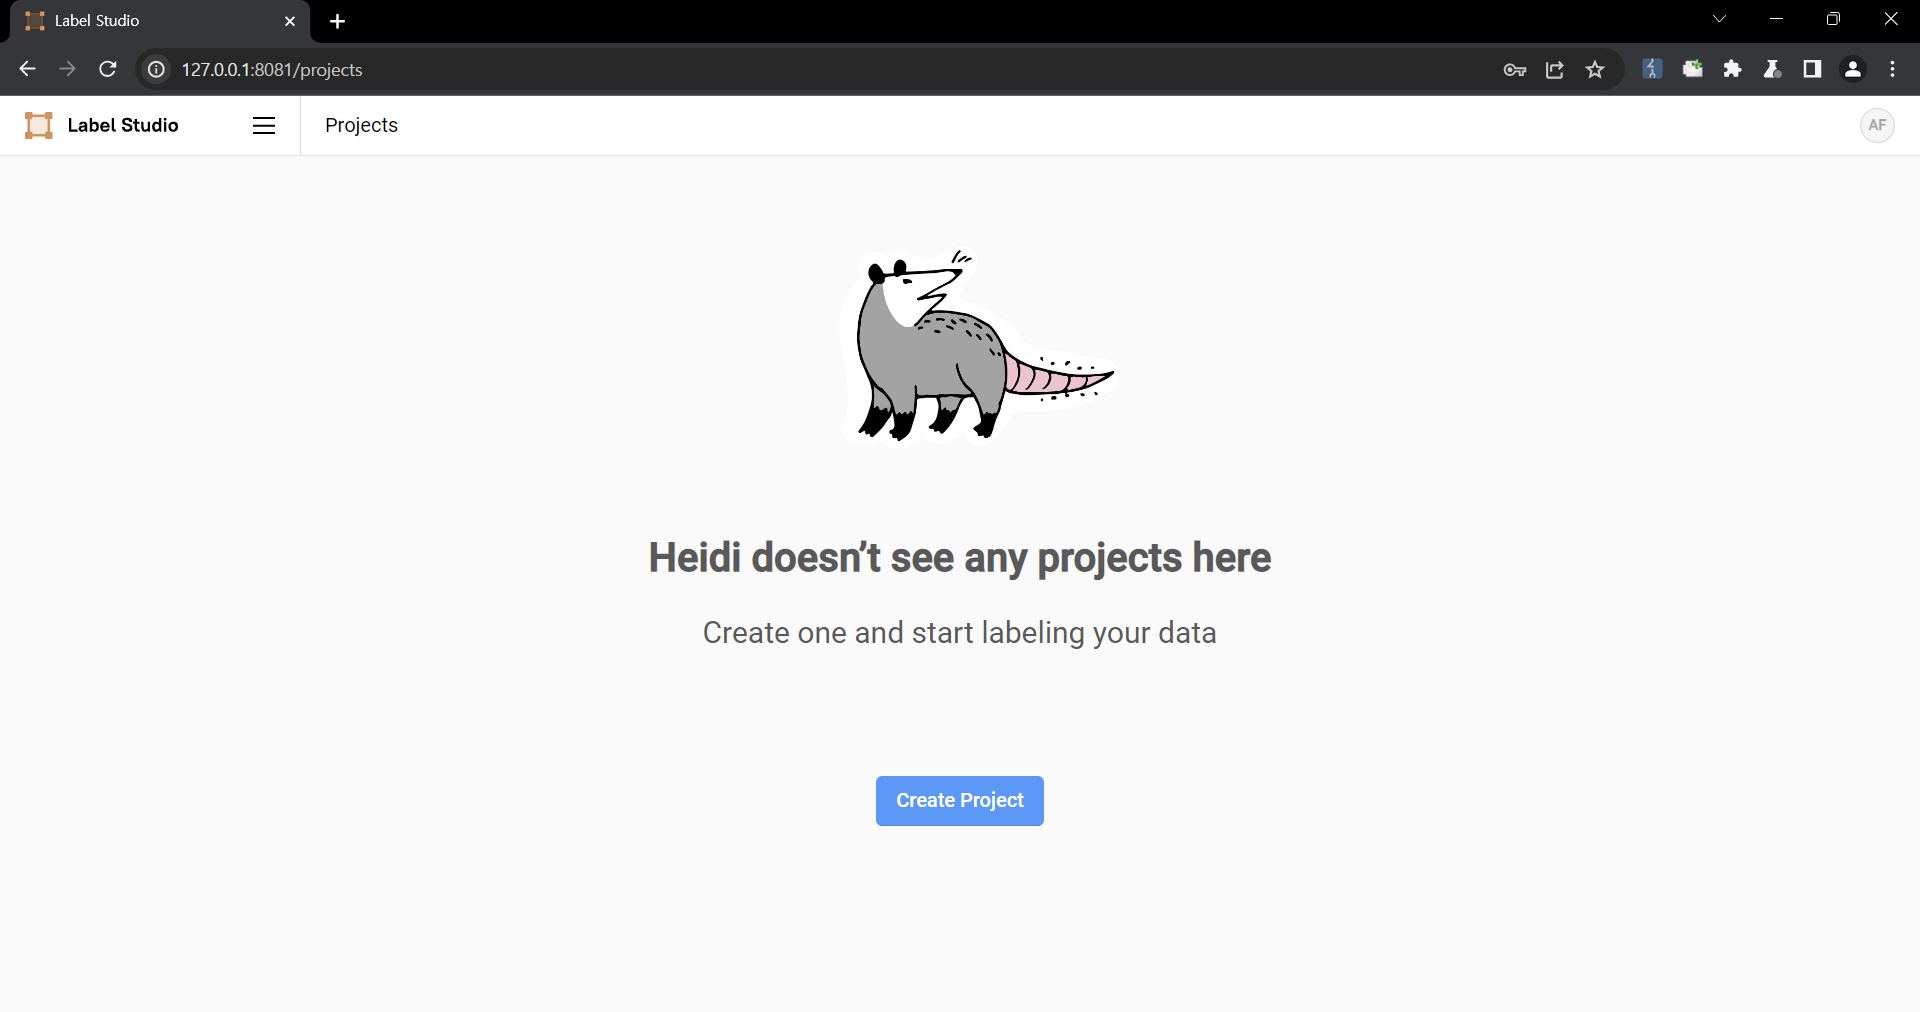
2. Upload a file containing the payload using the "Upload Files" function.